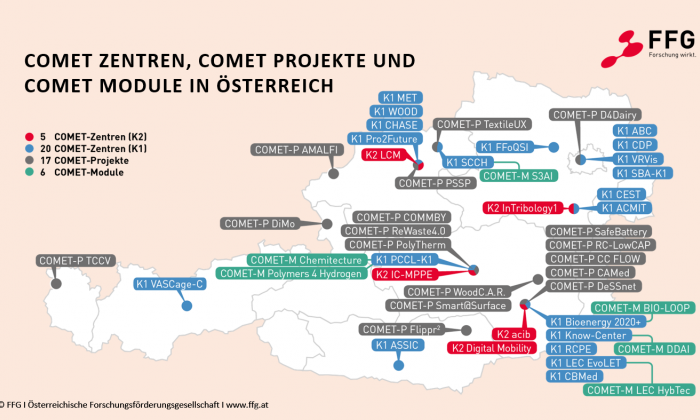
SBA Research is a research center for Information Security funded partly by the national initiative for COMET Competence Centers for Excellent Technologies.
The kick-off meeting of the FFG BRIDGE 1 project GASTRIC (Gene Anonymisation and Synthetisation for Privacy) took place on July 15th, 2020 at SBA Research. The GASTRIC project addresses the challenge to preserve the privacy of individuals taking part in microbiome studies… Read More
“TikTok collects a lot of user data. But other apps do that as well. You can use such data to influence political developments in other countries. […]” Read the full article at futurezone.at. Read More
The paper “Supporting complex decision making by semantic technologies“ by Stefan Fenz has won the best in-use paper award at ESWC20. ESWC20 was held online from June 2 – June 4, 2020. Congrats! You can find the paper here.
Digital approaches to proximity tracing on Smartphones are expected to contribute significantly to master the Covid-19 pandemic. Several approaches went live since May, and a heated discussion on centralised versus decentralised approaches arose. Beyond technical considerations, like their underlying working principle, constraints due to dependencies on the underlying hardware and… Read More
For many companies, the crisis was a rapid driver of digitalization – as a result, the hacker scene has experienced another real upswing. The topic of IT security has thus also gained in importance. As usual, participants will be provided with exciting community news, expert interviews, trends and the most… Read More
This document provides an overview of the architecture of the L-band Digital Aeronautical Communications System (LDACS), which provides a secure, scalable and spectrum efficient terrestrial data link for civil aviation. LDACS is a scheduled, reliable multi-application cellular broadband system with support for IPv6. N.Mäurer, T.Gräupl, C.Schmitt: L-band Digital Aeronautical Communications… Read More
Monsta FTP 2.10.1 or below is prone to a stored cross-site scripting vulnerability in the language setting due to insufficient output encoding. Read More
Monsta FTP 2.10.1 or below is prone to a server-side request forgery vulnerability due to insufficient restriction of the web fetch functionality. This allows attackers to read arbitrary local files and interact with arbitrary third-party services. Read More
Monsta FTP 2.10.1 or below allows external control of paths used in filesystem operations. This allows attackers to read and write arbitrary local files, allowing an attacker to gain remote code execution in common deployments. Read More
SBA Research, the Vienna Competence Center for Information Security, will be funded for another four years within the framework of COMET – Competence Centers for Excellent Technologies Report of the FFG On 16 June 2020, the mid-term evaluation of SBA-K1, the COMET flagship research program of SBA Research, took… Read More
Last week, our annual event for partners and friends of SBA Research, IMPACT, brought together experts, practitioners, and decision-makers from research, industry, and the open-source community. The afternoon provided an opportunity to discuss the latest developments in security, AI, and innovation, celebrate our long-standing relationships, and mark 20 years of SBA Research’s contributions to cutting-edge cybersecurity and trustworthy digital innovation. ∞
A group of dedicated young researchers presented their work at the 22st ICT Security Conference on 16 and 17 September 2026, which was organized by the Austrian Armed Forces. ∞
A new paper, “Automated Reasoning for Indistinguishability in the CCSA,” co-authored by Laura Kovács, key researcher at SBA Research and full professor at the Faculty of Informatics of the Vienna University of Technology (TU Wien), and Matteo Maffei, key researcher at SBA Research and Professor at TU Wien, has been accepted for presentation at the 33rd ACM Conference on Computer and Communications Security (CCS). ∞